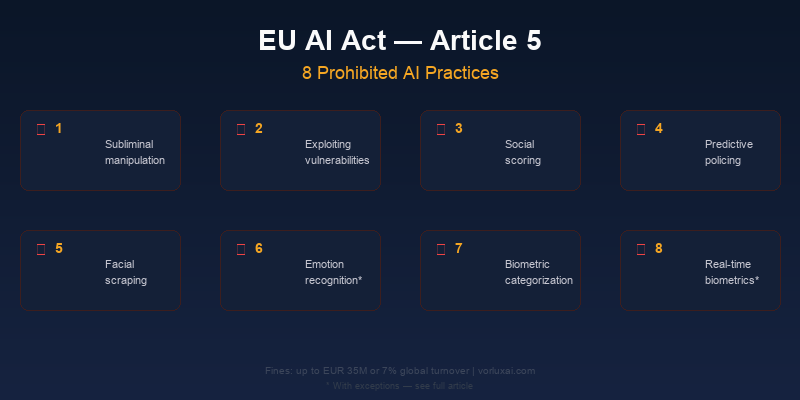
Article 5 of the EU AI Regulation (2024/1689) sets the hardest limits in the entire regulation. It defines 8 AI practices that have been completely banned in the European Union since February 2025.
The Digital Omnibus, Regulation (EU) 2026/1744 (in force since 27 July 2026), adds two more to Article 5 from 2 December 2026: AI systems that generate or manipulate realistic intimate or sexually explicit images of an identifiable person without their explicit consent (Art. 5(1)(ba)), and AI systems that generate child sexual abuse material (Art. 5(1)(bb)).
For everyday business uses (chat assistants, document search, transcription, code help) none of these applies. The decision tree below tells you in a few minutes whether yours is the exception.
Is Your AI Practice Prohibited? Decision Tree
flowchart TD
    A[Your AI System] --> B{Does it score people\nbased on social behavior?}
    B -->|Yes| C[PROHIBITED\nSocial Scoring]
    B -->|No| D{Does it use real-time\nbiometric surveillance?}
    D -->|Yes| E[PROHIBITED\nMass Surveillance]
    D -->|No| F{Does it exploit\nvulnerable groups?}
    F -->|Yes| G[PROHIBITED\nManipulative AI]
    F -->|No| H{Does it predict\ncriminal behavior?}
    H -->|Yes| I[PROHIBITED\nPredictive Policing]
    H -->|No| J[LIKELY PERMITTED\nCheck High-Risk List]

    style C fill:#FECACA,stroke:#B91C1C
    style E fill:#FECACA,stroke:#B91C1C
    style G fill:#FECACA,stroke:#B91C1C
    style I fill:#FECACA,stroke:#B91C1C
style J fill:#D1FAE5,stroke:#059669Not sure where you stand? Take the 3-minute EU AI Act checklist for SMEs.
1. Subliminal Manipulation (Art. 5.1.a)
Banned: AI systems that deploy subliminal techniques beyond a person’s consciousness to materially distort their behavior in a way that causes harm.
Real example: A shopping app using undetectable AI patterns to make users buy more than they want or need.
Your business: If you use AI for marketing, ensure recommendations are transparent and users understand why something is suggested.
2. Exploiting Vulnerabilities (Art. 5.1.b)
Banned: AI that exploits vulnerabilities of persons due to age, disability, or social/economic situation to distort their behavior.
Real example: A loan chatbot detecting a user’s financial anxiety and using that to pressure them into unfavorable terms.
Your business: If your AI interacts with vulnerable groups (elderly, disabled, minors), verify it doesn’t optimize toward harmful behaviors.
3. Social Scoring (Art. 5.1.c)
Banned: Evaluation or classification of persons based on social behavior or personal characteristics, resulting in unjustified detrimental treatment.
Real example: A system scoring employees based on social interactions outside work to decide promotions.
Your business: If you have employee or customer scoring, ensure criteria are relevant, proportionate, and non-discriminatory.
4. Predictive Criminal Risk Assessment (Art. 5.1.d)
Banned: AI assessing the risk of a person committing a crime based solely on profiling or personality traits (without objective verifiable facts).
Your business: If you use AI for fraud risk assessment, ensure it’s based on actual behaviors, not demographic profiles.
5. Untargeted Facial Scraping (Art. 5.1.e)
Banned: Creating facial recognition databases through untargeted scraping of images from the internet or CCTV.
Your business: If you use computer vision AI, don’t train models with faces collected without consent.
6. Emotion Recognition in Work/Education (Art. 5.1.f)
Banned: Emotion recognition systems in the workplace or educational institutions, except for medical or safety reasons.
Real example: Video conferencing software analyzing employee facial expressions during meetings to measure “engagement.”
Exception: A system detecting fatigue in heavy machinery operators for safety IS permitted.
7. Biometric Categorization (Art. 5.1.g)
Banned: Systems categorizing persons based on biometric data to infer race, political opinions, trade union membership, religion, sexual orientation, or other protected categories.
Your business: If you use vision AI, ensure it doesn’t classify people by protected attributes.
8. Real-Time Biometric Identification (Art. 5.1.h)
Banned: Real-time remote biometric identification in publicly accessible spaces by law enforcement, except in strictly necessary cases: searching for victims, terrorist threats, or serious crime suspects with judicial authorization.
Your business: If you’re not law enforcement, this doesn’t directly apply. But if you install AI cameras, ensure they don’t perform real-time facial recognition.
What to Do If You Detect a Prohibited Practice
- Stop the system immediately
- Document what system it was, what it did, and since when
- Notify your AI compliance officer
- Assess whether harm was caused to persons
- Remediate and prevent recurrence
- Consult legal counsel on authority notification obligations
Quick Checklist
- I’ve reviewed all AI systems against the 8 prohibited practices
- No system uses subliminal manipulation
- We don’t exploit vulnerabilities of any group
- We don’t have social scoring of employees or customers
- We don’t do predictive criminal risk assessment without facts
- We haven’t created facial databases through scraping
- We don’t do emotion recognition at work (without medical/safety exception)
- We don’t biometrically categorize by protected attributes
- We don’t do real-time biometric identification in public spaces
The Local AI Advantage
As LegalNodes explains, businesses that fail to audit their AI systems face both regulatory and reputational risk. When your AI runs on your own hardware, Article 5 compliance is much simpler:
- Full control over what the model does
- No risk of provider updates introducing prohibited practices
- Complete audit trail of every interaction
- No dependency on third parties who may change model behavior
Evaluate your EU AI Act compliance →
VORLUX AI | vorluxai.com | We deploy AI that complies with the EU AI Act by design.
Penalties
These are the highest fines in the regulation: up to EUR 35 million or 7% of global annual turnover, whichever is higher; for SMEs the lower of the two applies (Art. 99(3) and 99(6)). The ban has applied since February 2025 and enforcement is active. The practical answer is the decision tree above: if every answer is “no”, Article 5 is not your problem.
Next steps
- Audit your current AI systems against the 8 prohibited practices
- Follow the five steps to remediate if you detect a prohibited practice
- Use the checklist to verify no system uses subliminal manipulation or exploits vulnerabilities
- Review how to classify your AI risk level correctly
- Learn more about the role of Spain’s AI watchdog and how local deployment supports GDPR
Related reading
- GDPR and AI in 2026: Local Deployment Is the Clean Answer
- AESIA: What Every Spanish Business Deploying AI Must Know in 2026
- How to Classify Your AI’s Risk Level Under the EU AI Act (Art. 6)
- Grab the template: Prohibited practices checklist (Article 5).
Sources
- Regulation (EU) 2024/1689, Article 5
- EU AI Act: Official Resource
- The EU AI Act Implementation Timeline: Kennedys Law
- EU AI Act 2026 Updates and Compliance Requirements: LegalNodes
Not sure if your AI system falls under these prohibitions? Schedule a free compliance assessment: we help European businesses navigate the EU AI Act with confidence.
Work with us
We size the model and the machine by measuring, not by guessing. If you want to see your own task running on real hardware, book a 15-minute call or see how we work in consulting.