By the end of this post you will know which of the four risk categories of the EU AI Act each of your AI systems falls into, and what obligations come with it. Article 6 is the cornerstone of that classification. You get a decision tree, examples and a checklist to document it.
flowchart TD
    A["Your AI System"] --> B{"Is it a prohibited\npractice?\n(Art. 5)"}
    B -->|Yes| C["PROHIBITED\nDo not use (Art. 5)"]
    B -->|No| D{"Safety component of\nan Annex I product?"}
    D -->|Yes| E["HIGH RISK\nFull compliance required"]
    D -->|No| F{"Annex III\nuse case?"}
    F -->|Yes| G{"Does Art. 6(3)\nexception apply?"}
    G -->|Yes| H["LIMITED RISK\nTransparency obligations"]
    G -->|No| E
    F -->|No| I{"Interacts with people\nor generates content?"}
    I -->|Yes| H
    I -->|No| J["MINIMAL RISK\nNo specific obligations"]
    style C fill:#FECACA,stroke:#B91C1C
    style E fill:#FEF3C7,stroke:#F5A623
    style H fill:#DBEAFE,stroke:#2563EB
style J fill:#D1FAE5,stroke:#059669Not sure where you stand? Take the 3-minute EU AI Act checklist for SMEs.
The 4 risk categories
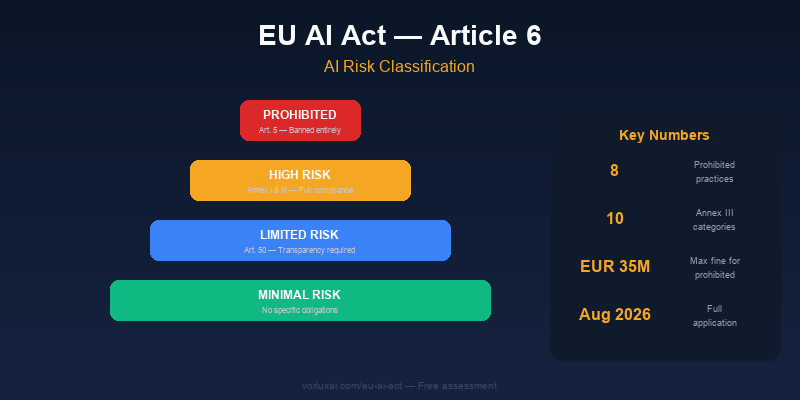
Level 1: Prohibited (Art. 5)
Completely banned in the EU. Social scoring, subliminal manipulation, workplace emotion recognition, untargeted facial scraping.
Your obligation: Don’t use. If detected, stop immediately.
Level 2: High risk (Art. 6 + Annexes I & III)
Can be used but require full compliance: technical documentation, conformity assessment, human oversight, EU database registration. After the Digital Omnibus, Regulation (EU) 2026/1744, Annex III obligations apply from 2 December 2027 and Annex I from 2 August 2028, time enough to classify carefully and document once.
Via Annex I (product safety): AI as safety component of machinery, toys, medical devices, vehicles, aviation.
Via Annex III (use case): Biometrics, critical infrastructure, education, employment, essential services, law enforcement, migration, justice.
Exception Art. 6(3): Even Annex III systems are NOT high-risk if they perform narrow procedural tasks, improve prior human work, detect patterns without replacing human judgment, AND don’t create significant risk.
Level 3: Limited risk (Art. 50)
Transparency obligations only. The provider must make sure people know they’re interacting with AI (Art. 50(1)) and that generated content is marked (Art. 50(2)); the deployer must disclose deepfakes and AI-generated text published to inform the public without human review (Art. 50(4)).
Examples: Chatbots, content generators, virtual assistants.
Level 4: Minimal risk
No specific obligations. Free use.
Examples: Spam filters, product recommendations, text correction, internal document classification.
Quick decision tree
- Prohibited practice (Art. 5)? → YES = BANNED
- Safety component of Annex I product? → YES = HIGH RISK
- Annex III use case? → YES = check Art. 6(3) exception
- Exception applies → LIMITED RISK
- No exception → HIGH RISK
- Interacts with people or generates content? → YES = LIMITED RISK
- None of the above → MINIMAL RISK
Classification checklist
For each AI system:
- Listed in AI systems inventory
- Checked against 8 prohibited practices (Art. 5)
- Checked against Annex I products
- Checked against Annex III use cases
- Art. 6(3) exception evaluated if applicable
- Classification documented with justification
- Responsible person assigned
- Next review date set
What changes if you’re high-risk
| Requirement | What to do | Article |
|---|---|---|
| Risk management | Continuous system | Art. 9 |
| Data governance | Training data quality | Art. 10 |
| Technical documentation | Complete Annex IV docs | Art. 11 |
| Record-keeping | Automatic system logs | Art. 12 |
| Transparency | Inform deployers | Art. 13 |
| Human oversight | Override mechanism + supervisor | Art. 14 |
| Accuracy | Performance and robustness | Art. 15 |
| Conformity | Assessment before market | Art. 43 |
| Registration | EU database entry | Art. 49 |
Practical example: Classifying a customer service chatbot
Suppose your company deploys an AI chatbot on your website to answer customer questions about product availability and returns. How would you classify it?
- Prohibited (Art. 5)? No. It does not perform social scoring, subliminal manipulation, or any banned practice.
- Safety component of an Annex I product? No. It is a standalone software tool, not embedded in machinery or a medical device.
- Annex III use case? Potentially: Annex III covers “AI systems intended to interact with natural persons.” However, a standard customer support chatbot that answers FAQs does not fall under the high-risk subcategories (biometrics, critical infrastructure, employment decisions, etc.).
- Art. 6(3) exception? Even if loosely related to Annex III, the chatbot performs narrow procedural tasks (looking up order status), improves prior human work (redirecting to agents when needed), and does not create significant risk to health, safety, or fundamental rights. The exception applies.
- Interacts with people? Yes: users chat with it directly.
Classification: Limited risk (Art. 50). The obligation is transparency: whoever provides the chatbot must make sure users know they are interacting with an AI system, not a human (Art. 50(1)). If you built it, or offer it under your own name, that’s you. A simple banner such as “You are chatting with an AI assistant” satisfies this requirement.
If that same chatbot were used to screen job applicants or assess creditworthiness, the classification would jump to high risk because those fall squarely under Annex III categories (employment, essential services). Context determines classification, not the technology itself.
Penalties
Fines under the Act scale with the category, and the checklist above is how you stay well clear of them. The amounts are set in Article 99 of Regulation (EU) 2024/1689:
- Prohibited practices (Art. 5): up to EUR 35 million or 7% of global turnover.
- Misclassification: can cost you up to EUR 15 million.
The local AI advantage
When AI runs on your local hardware:
- Easier classification: you control exactly what the model does
- Simpler documentation: no provider dependency
- Direct oversight: full access to model behavior
- Less regulatory risk: no third-party data transfers
Next step
Not sure where your AI falls? Take our interactive assessment:
Evaluate my EU AI Act compliance →
Request professional classification →
VORLUX AI | vorluxai.com | AI that complies with the EU AI Act by design.
Sources:
- Regulation (EU) 2024/1689, Articles 5-6
- EU AI Act Official Portal
- Gibson Dunn: EU AI Act Omnibus: postponed high-risk deadlines
- EU AI Act Compliance Guide: GDPR Register
Next steps
- Review the 8 prohibited practices to ensure your system is not banned
- Use the decision tree to check if your AI is a safety component
- Complete the classification checklist for every system in your inventory
- Check the specific requirements for high-risk systems
Related reading
- The 8 Prohibited AI Practices Under the EU AI Act (With Examples)
- AESIA: What Every Spanish Business Deploying AI Must Know in 2026
- The EU AI Act Calendar After the Digital Omnibus
- Grab the template: AI risk classification worksheet.
Work with us
VORLUX AI helps Spanish and European businesses deploy AI solutions that stay on your hardware, under your control. Whether you need hardware sizing, a local model running in production, or help staying on the right side of the EU AI Act, we can help.
We can classify your systems with you in a 15-minute call: book a call or see how we work.